Best Personal VPN for Linux: Your Own Server, Dedicated IP, Open-Source Clients
If you’re running Linux and need a high-quality, reliable, and the best VPN for Linux, you’ve come to the right place. Let’s get down to business. WireGuard, OpenVPN, IKEv2/IPSec, OpenConnect, Outline, VLESS+Reality (Xray-core), Hiddify. What we know for setting up your own VPN server on Linux using fully open-source software. Since you need your own server with dedicated IP address and privacy, so traditional commercial VPN providers aren’t right for you. You can do all of this on your own server, which you’ll need to rent from a hosting provider and set up yourself. But what if you don’t want to spend several hours setting it up yourself, yet still want to have a properly configured VPN and access to the server? The answer is simple — the Self Hosted Project (SHP). SHP isn't just another VPN app for Linux. Each client gets its own server with encryption, root access, a dedicated IP address, the ability to automatically configure various protocols, and the ability to change locations. Connect via any protocols available for Linux.
Key VPN Features on Linux
Let’s learn more about how VPN works within the Linux architecture first.
The Architectural Level
The VPN is integrated into the Android architecture through the official system framework VPNService API. The system reserves an isolated virtual interface (TUN) for VPN. This allows an app to centralize filtering and redirecting the outgoing traffic of the device.
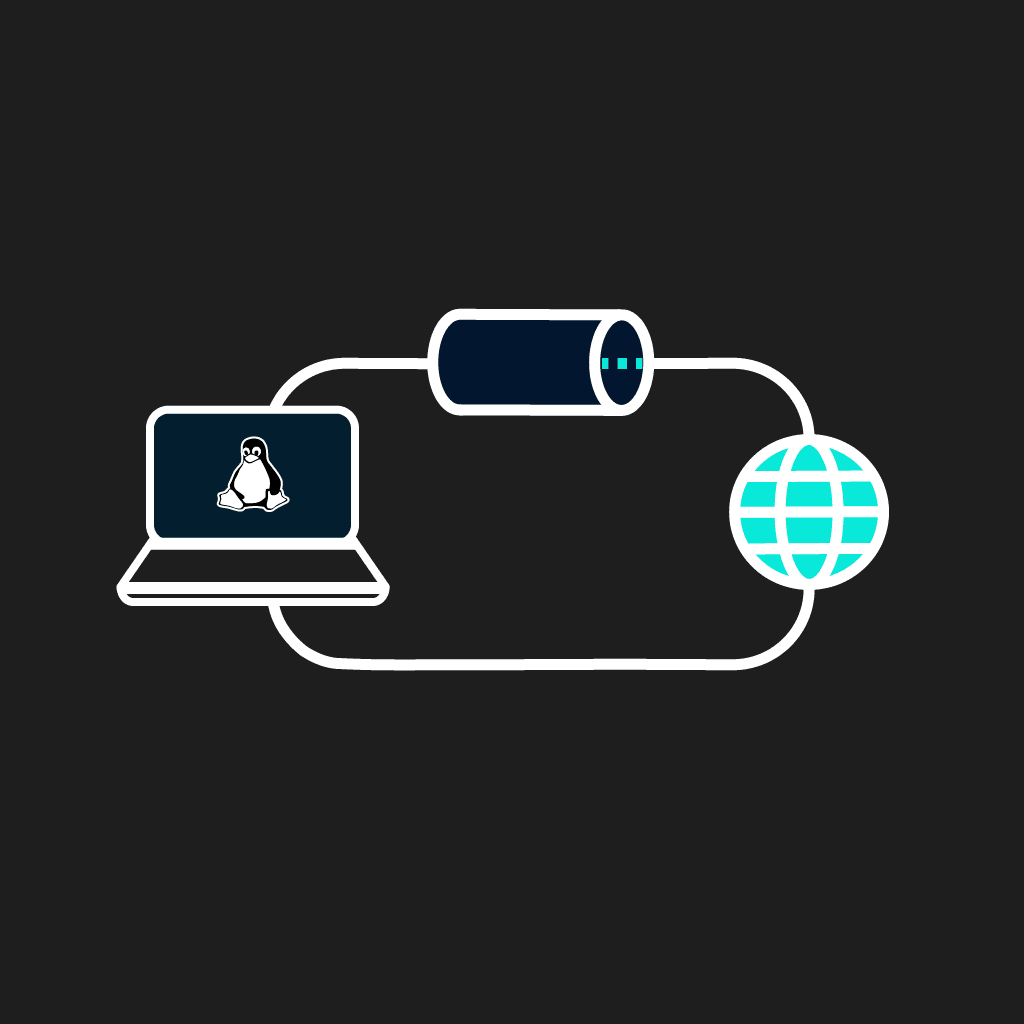
Split-Tunneling
Linux split tunneling for VPN allows you to route selected traffic to go through an encrypted VPN tunnel while letting other applications or local subnets directly access the public internet. This is great for local device discovery on the LAN, speeds up non-sensitive downloads, and replicates local service with regional restrictions
Kill-Switch
A network switch on Linux (moving from a home Wi-Fi network to a mobile network hotspot or a public Wi-Fi network) can trigger a race condition that allows people to see your unsecured traffic, real IP address, and DNS requests as the default routing table is overwritten by a new external network before the VPN tunnel is restored.
What makes SHP different from other shared VPN?
So, you've decided to get a VPN for Linux. Right away, offers from NordVPN and ExpressVPN start popping up online. Are these offers worth considering? First of all, prices go up after just one year, making the VPN expensive for you. Second, any additional features always come at an extra cost—for example, a dedicated IP address. Third, there’s a limit on the number of connected devices. Why is SHP the best solution for you? Here are three key differences from NordVPN and ExpressVPN:
- You get your own VPS instead of a shared server;
- a dedicated IP at no extra charge;
- root access, so you can verify that no logs are kept.
That's a pretty good start for using our VPN service.
How to set up a VPN on Linux in 3 steps
You've made up your mind. But what's next? How do you sign up for the service? Setting up a VPN on Linux isn't as simple as clicking the “Connect”, but it's pretty simple with SHP — no need to go through a lengthy verification process or wait all day for confirmation from the server. Registration is stress-free and comes with no additional requirements. Let us walk you through the process in three steps.
SELECT
Sign up, select a protocol, a plan, and a server location, then pay with cryptocurrency or a credit card.
GET
Access the VPN configuration files and the server itself via the web panel.
CONNECT
Connect your Linux device to your VPN server. And note that it all happens very quickly: the whole process takes just 10 minutes.
Which VPN protocol should I use on Linux?
To select a protocol, review its features and specifications of Linux VPN client software. Compare these specifications across different protocols.
WireGuard
If you want the fastest VPN speeds and the lowest CPU load on Linux, go with WireGuard. It’s already baked into the Linux kernel, so you get smooth integration and great resource efficiency. WireGuard’s Linux lean code means you can push more data with less strain on your hardware, and if you hop between networks, it reconnects almost instantly.
OpenVPN
But sometimes you’re stuck behind a strict firewall or a public network that blocks typical VPN traffic. That’s when OpenVPN Linux comes in handy. It plays nice with restrictive environments, sneaking through ports like TCP 443 that most networks leave open. OpenVPN’s Linux track record speaks for itself—it’s been audited for over twenty years, so people trust its stability and security. Just keep in mind, it’s heavier than WireGuard Linux. You’ll notice higher CPU usage and slower top speeds. Still, it’s a solid backup when you really need it.
OpenConnect VPN
OpenConnect VPN is a free, open-source VPN client designed as an alternative to Cisco’s proprietary AnyConnect client. It is used to securely connect to corporate and private networks by disguising traffic as a standard HTTPS request (via SSL/TLS ports), which makes it easy to bypass blocks, ISP firewalls, and NAT restrictions.
Why a personal VPN server is the best choice for Linux users
Running your own VPN for Linux server — no more worrying about some commercial provider logging your traffic, capping your speeds, or stuffing your system full of bulky client apps. On Linux, everything just plugs right in. WireGuard, for example, slips right into the kernel with systemd handling service control, so setup’s clean and efficient. There are four specific advantages to choosing a best VPN for Linux:
- Dedicated IP;
- Root access to your server—you can check the logs and customize the configuration to suit your needs;
- Isolated connection—no neighbors;
- One VPS for all your devices: laptop, desktop, router, and server.
Performance-wise, there’s a lot to love. With Wireguard running at the kernel level, you get blazing speeds and barely any CPU load. Since you’re not sharing space with random users, you don’t deal with throttling or surprise bandwidth limits. Want to get fancy? Go ahead—write scripts for split tunneling, lock down your firewall with nftables or iptables, or tweak your DNS. It’s all under your control.
Linux compatibility and supported distributions
Since we don't use our own application but rather official open-source ones, you can use our service on all modern Linux distributions, such as: Ubuntu, Debian, Fedora, Arch Linux, Linux Mint, openSUSE, Raspberry Pi OS, CentOS—you get the picture. You mostly see two main architectures in play: x86_64 (your typical desktop and laptop hardware) and ARM (which shows up in a lot of low-power devices like smartphones, Raspberry Pis, or even some newer laptops).
What you can do with a personal VPN on Linux
You can fine-tune the settings and access experimental features that no other VPN provider offers—and you can configure everything at any time via the CLI. By using a VPN, you’ll gain access to content that’s unavailable in your country and hide the websites you visit from your ISP.
Self-host services through your VPN tunnel
When you self-host services and connect through a private VPN tunnel, you’re basically putting a secure, encrypted shield around your home apps—think things like Nextcloud for files, Jellyfin for streaming, or Home Assistant for your smart devices. The best part? On your own VPS with root access, you can set up your own services (Nextcloud, Bitwarden, Jellyfin, Git server) alongside a VPN tunnel. This is unique—it’s not possible with competitors’ shared hosting plans.
Protect your laptop on public Wi-Fi
When you’re using public Wi-Fi, you have to watch your back—these networks aren’t as safe as they seem. Start with encrypting your data traffic; a VPN goes a long way here, shielding your information from snoops lurking on the same network. Cafés, airports, hotels—open networks. On public Wi-Fi, most of your traffic is already encrypted by HTTPS — but your DNS requests and the domains you connect to (via SNI) are still visible to anyone on the same network. A VPN hides that too, so no one watching the network knows which sites you're visiting.
Access banking and work resources securely
To securely access banking services and work resources via a VPN, it is important to use a reliable commercial solution or a corporate VPN for Linux, follow recommendations for choosing a server, and not neglect additional security measures, such as multi-factor authentication. If you regularly work from abroad, you should consider a VPN with a dedicated IP address. A static IP address makes your login history more consistent and reduces the likelihood that the bank will flag your login as suspicious. Connecting to a server located in your country or city helps avoid being flagged for suspicious activity. Logging into your bank account via an IP address from another country may trigger security systems, result in a temporary account lockout, or require additional identity verification.
SHP vs free VPN apps for Linux
To compare SHP and free VPN services for Linux, you can review their features:
| Free Linux VPN | Typical paid Linux VPN | SHP personal VPN server | |
|---|---|---|---|
| No traffic logs | |||
| Isolated bandwidth | |||
| Ads | |||
| Dedicated IP | For an additional price | ||
| Root access | |||
| Supported protocols | 1-2 | 2-4 | 7 |
Use SHP on other devices
SHP provides you with a server that comes with pre-configured settings, to which you can connect any devices that support the protocol you've selected, so a single configuration works everywhere. It works on Windows OS, iOS, and MacOS devices too. SHP allows you to use a single subscription on multiple devices at once. By default, SHP provides between 10 and 32 configuration files for connecting to a VPN (depending on the protocol), but if you need more, you can connect to the server and generate as many additional files as you need.
Frequently asked questions
We use only official open-source applications; you can find download links on the /get-started page or in your server's dashboard.
Yes. Support depends not on SHP, but on the protocol clients—they are available in all major distributions via standard repositories.
Yes. SHP operates entirely via the CLI (wg, openvpn, systemd-networkd). This is convenient for headless servers, Raspberry Pi devices, and automation via scripts.
No. Every plan is a real VPS with specific features provided by SHP on dedicated IP. However, if cost is a major concern for you or your project has a limited budget, we can offer you a suitable, budget-friendly alternative: a monthly plan with no long-term commitments.
WireGuard is generally considered the best choice for Linux due to its direct integration into the system kernel, high performance, and compact architecture. Included in the Linux kernel since version 5.6—offers minimal overhead and simpler configuration. OpenVPN for Linux is more versatile and works better through strict firewalls. Both are available on SHP.
Setting up WireGuard on Linux is quite simple. Just install the WireGuard package using your distribution’s package manager (such as apt, dnf, or pacman), then download the configuration file from the SHP control panel and place it in the /etc/wireguard/ directory. After that, all that’s left is to activate the VPN connection using the `wg-quick up` command, specifying the name of the corresponding configuration file. If everything is done correctly, a secure connection will be established in just a few seconds.
Yes. Raspberry Pi OS fully supports both WireGuard and OpenVPN without the need to install any non-standard components. Setting up both VPN protocols is virtually identical to configuring them on a regular Linux computer, so users familiar with desktop distributions will quickly get the hang of it. The configuration is installed the same way as on a desktop. The section on routing traffic through the Pi for the entire local network is a bonus.
WireGuard delivers higher performance because it runs directly in the Linux kernel, OpenVPN uses more resources, but on modern hardware, you won't even notice it. On an SHP VPS, each user is provided with resources, so the network bandwidth is not shared with other customers. This ensures consistent performance and predictable connection speeds. The close location means low ping.
Yes, it’s safe. If you wish, you can sign up without providing an email address or completing the KYC process, and make payments using cryptocurrency, which allows you to maintain a high level of privacy. An additional benefit is that you are granted full root access to the server. This allows you to independently review system logs, monitor service operations, and verify what data is being processed and stored. Trusted open-source VPN clients, such as WireGuard and OpenVPN, are used for the connection.